Search
Search projects, tokens and protocols by name or address
 Haust Network
Badges
About
Haust Network is a Layer 2 blockchain built on the Polygon CDK, integrating with the Agglayer and Account Abstraction from the outset.
Badges
About
Haust Network is a Layer 2 blockchain built on the Polygon CDK, integrating with the Agglayer and Account Abstraction from the outset.
Why is the project listed in others?
Consequence: projects without a data availability bridge fully rely on single entities (the sequencer) to honestly rely available data roots on Ethereum. A malicious sequencer can collude with the proposer to finalize an unavailable state, which can cause loss of funds.
Consequence: projects without a proper proof system fully rely on single entities to safely update the state. A malicious proposer can finalize an invalid state, which can cause loss of funds.
Learn more about the recategorisation here.
Funds can be stolen if
Funds can be lost if
Users can be censored if
There is no mechanism to have transactions be included if the sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. is down or censoring. Although the functionality exists in the code, it is currently disabled.
Currently the system permits invalid state rootsA cryptographic hash succinctly representing a state using a Merkle tree.. ‘Pessimistic’ proofs only validate the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. accounting.
Proof construction and state derivation rely fully on data that is NOT published onchain.
There is no window for users to exit in case of an unwanted upgrade since contracts are instantly upgradable.
Only the whitelisted proposers can publish state rootsA cryptographic hash succinctly representing a state using a Merkle tree. on L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development., so in the event of failure the withdrawals are frozen.
Data is not stored on chain
Transaction data is kept off-chain. BridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. accounting is protected by pessimistic proofs while L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups. state transitions are not proven on Ethereum.
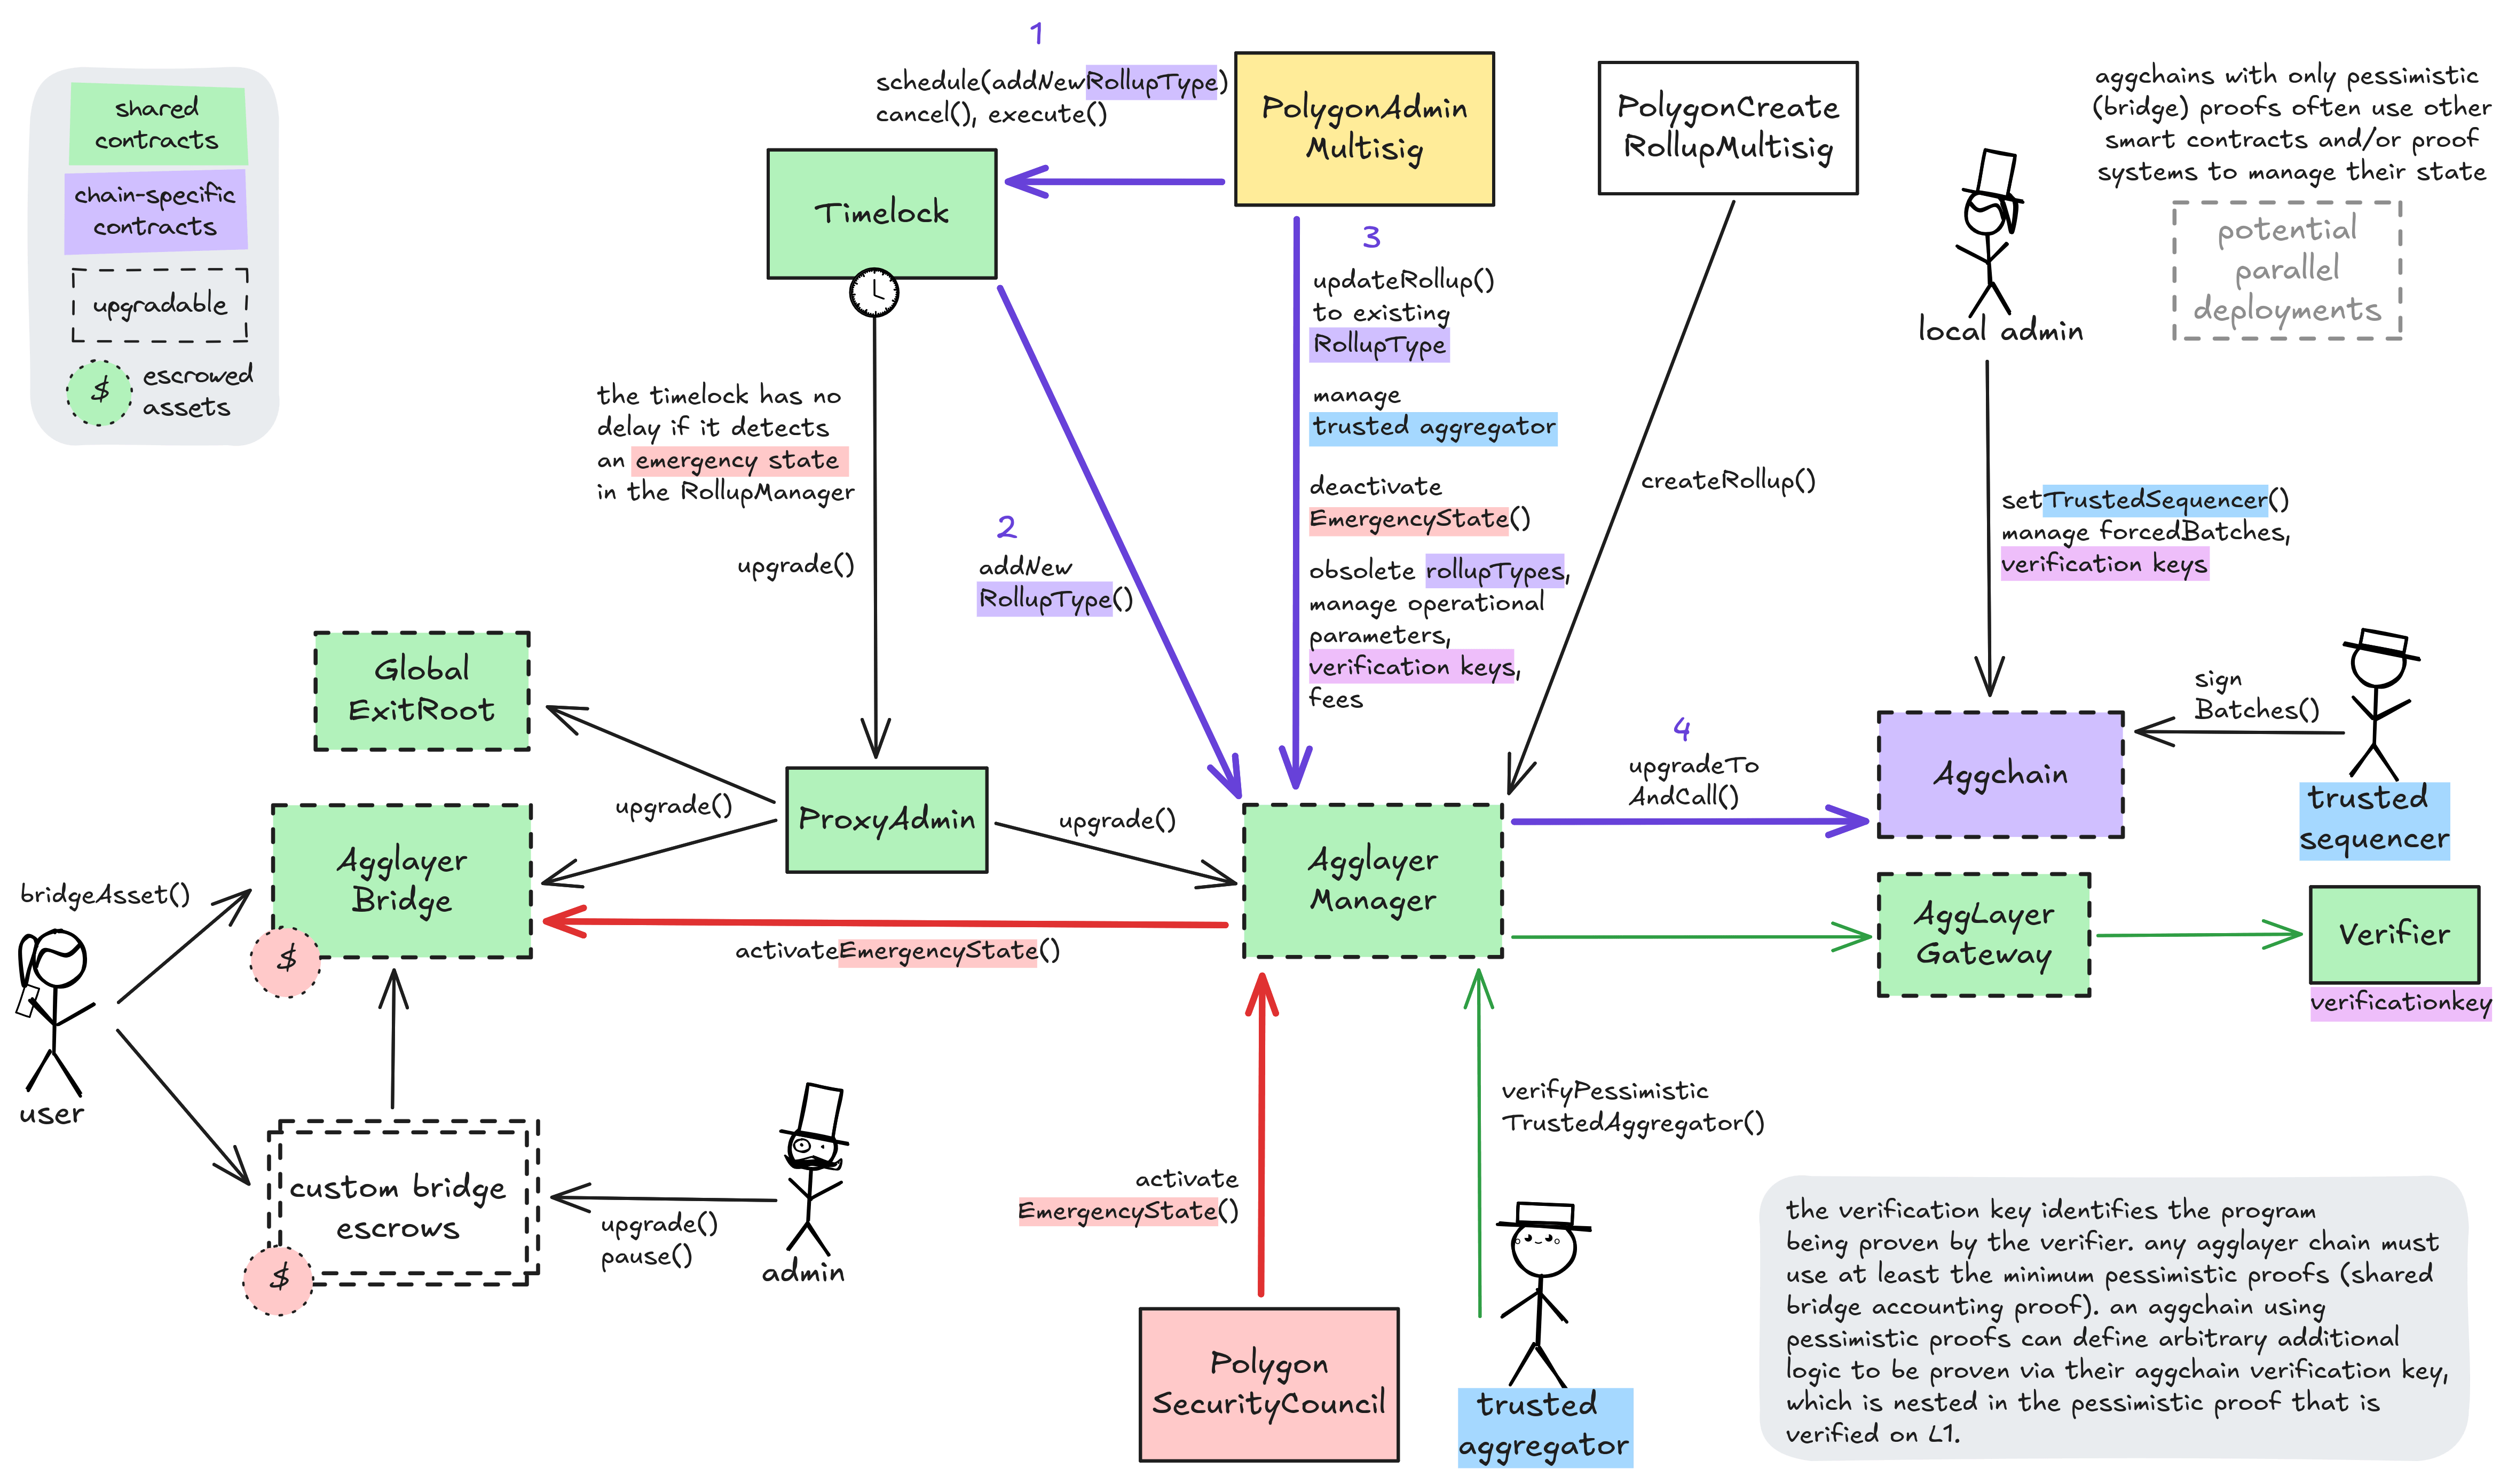
The regular upgrade process for shared system contracts and L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.-specific validiumAn off-chain solution that uses validity proofs for settlement and publishes the data offchain, therefore requiring an additional trust assumption. contracts starts at the Polygon
The Polygon
Furthermore, the Polygon
Past upgrades
The metrics include upgrades on the currently used proxy contracts. Historical proxy contracts and changes of such are not included.
5changesinitital disco of a no-proof others agglayer chain.
initital disco of a no-proof others agglayer chain.
Initial discovery
| + | Status: CREATED |
| reference AgglayerGateway (eth:0x046Bb8bb98Db4ceCbB2929542686B74b516274b3) | |
| +++ description: None | |
| + | Status: CREATED |
| reference AgglayerBridge (eth:0x2a3DD3EB832aF982ec71669E178424b10Dca2EDe) | |
| +++ description: None | |
| + | Status: CREATED |
| reference AgglayerManager (eth:0x5132A183E9F3CB7C848b0AAC5Ae0c4f0491B7aB2) | |
| +++ description: None | |
| + | Status: CREATED |
| reference AgglayerGER (eth:0x580bda1e7A0CFAe92Fa7F6c20A3794F169CE3CFb) | |
| +++ description: None | |
| + | Status: CREATED |
| contract AggchainECDSAMultisig (eth:0xaD83Cd3e5A725546daDC5A25088c5c098d320Ca8) | |
| +++ description: System contract defining the Haust Network Aggchain logic. It only enforces bridge accounting (pessimistic) proofs to protect the shared bridge while the Aggchain state transitions are not proven. They must instead be signed by 1 aggchainSigner(s). | |
Users can't force any transaction
There is no general mechanism to force the sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. to include the transaction.
Users can be censored if the operator refuses to include their transactions.
Regular messaging
The user initiates L2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups.->L1Layer 1 (L1) is a blockchain that is self-reliant on its validator set for its security and consensus properties. Ethereum is an example of a layer 1. Blockchains started receiving the moniker of layer 1 once layer 2 became a meaningful area of development. messages by submitting a regular transaction on this chain. When the blockAn ordered list of transactions and chain-related metadata that gets bundled together and published to the L1/DA layer. Nodes execute the transactions contained within blocks to change the rollup chain’s state. Protocol rules dictate what constitutes a valid block, and invalid blocks are skipped over. containing that transaction is settled, the message becomes available for processing on L1. ZK proofs are required to settle blocks.
Shared bridge and Pessimistic Proofs
Polygon Agglayer uses a shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. escrow for Rollups, Validiums and external chains that opt in to participate in interoperabilityRefers to the capability of different blockchain networks to communicate and share data. It enables the transfer of assets and information between blockchains, facilitating functionality and collaboration between blockchain ecosystems.. Each participating chain needs to provide zk proofs to access any assets in the shared bridge. In addition to the full execution proofs that are used for the state validation of Rollups and Validiums, accounting proofs over the bridges state (Polygon calls them ‘Pessimistic Proofs’) are used by external chains (cdk-erigon-sovereign and cdk-opgeth-sovereign variants). Using the SP1 zkVMA special type of zk proving system that proves the correctness of state transitions of a virtual machine. Computation is represented by a program in a specific instruction language, it can have private and public inputs and public outputs. Most of zkVMs are STARKs. by Succinct, even projects without a full proof systemThe infrastructure that allows projects to verify their state transitions. It is composed by onchain verifiers and offchain provers. The main two flavors are optimistic and ZK proof systems, but they can be combined in a hybrid model. In general though, if a system is able to accept state roots optimistically, even if it has a ZK component, it is considered an optimistic proof system. on Ethereum are able to share the bridge with any other Aggchain without adding additional trust assumptions.
Funds can be lost if the accounting proof system for the bridge (pessimistic proofs, SP1) is implemented incorrectly.
Funds can be stolen if the operator manipulates the L2 state, which is not validated on Ethereum (CRITICAL).
Ethereum
Actors:
A Multisig with 5/9 threshold.
- Can upgrade with 3d delay
- AgglayerGateway Timelock with 3d delay (no delay if in emergency state) → Shared
Proxy Admin - AgglayerBridge Timelock with 3d delay (no delay if in emergency state) → Shared
Proxy Admin - AgglayerManager Timelock with 3d delay (no delay if in emergency state) → Shared
Proxy Admin - AgglayerGER Timelock with 3d delay (no delay if in emergency state) → Shared
Proxy Admin
- AgglayerGateway Timelock with 3d delay (no delay if in emergency state) → Shared
- Can interact with AgglayerGateway
- add new routes from proof selector to verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. / pessimisticVkey for pessimistic proofs with 3d delay Timelock with 3d delay (no delay if in emergency state)
- add or update default aggchain verification keys (aggchainVkey) for any given selectors
- change the aggchainSigners and threshold (a multisig used for permissioned state transitions)
- freeze routes from proof selector to verifier / pessimisticVkey for pessimistic proofs
- Can interact with AgglayerBridge
- upgrade the implementation of wrapped tokens deployed by the bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. with 3d delay Timelock with 3d delay (no delay if in emergency state)
- Can interact with AgglayerManager
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the Polygon
Rollup Manager - manage all access control roles, add new rollup types (which are implementation contracts that can then be upgraded to by connected projects), update any connected projects to new rollup types, migrate to pessimistic proofs and rollback batches, connect existing rollups to the Polygon
Rollup Manager with 3d delay Timelock with 3d delay (no delay if in emergency state) - manage parameters like fees for all connected projects, set the trusted aggregator, stop the emergency state, update projects and obsolete rollup types
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the Polygon
- Can interact with Timelock
- propose, cancel and execute transactions in the timelock, manage all access control roles and change the minimum delay with 6d delay or with 3d delay Timelock with 3d delay (no delay if in emergency state) with 3d delay (no delay if in emergency state) - or - acting directly with 3d delay (no delay if in emergency state)
Participants (9):
0xEB5E…EA720xAb35…235E0xf02B…D4B20xdFEd…56Da0xffbf…32380xeD44…dB370x516e…46B70x2161…d4170x8B9F…782B
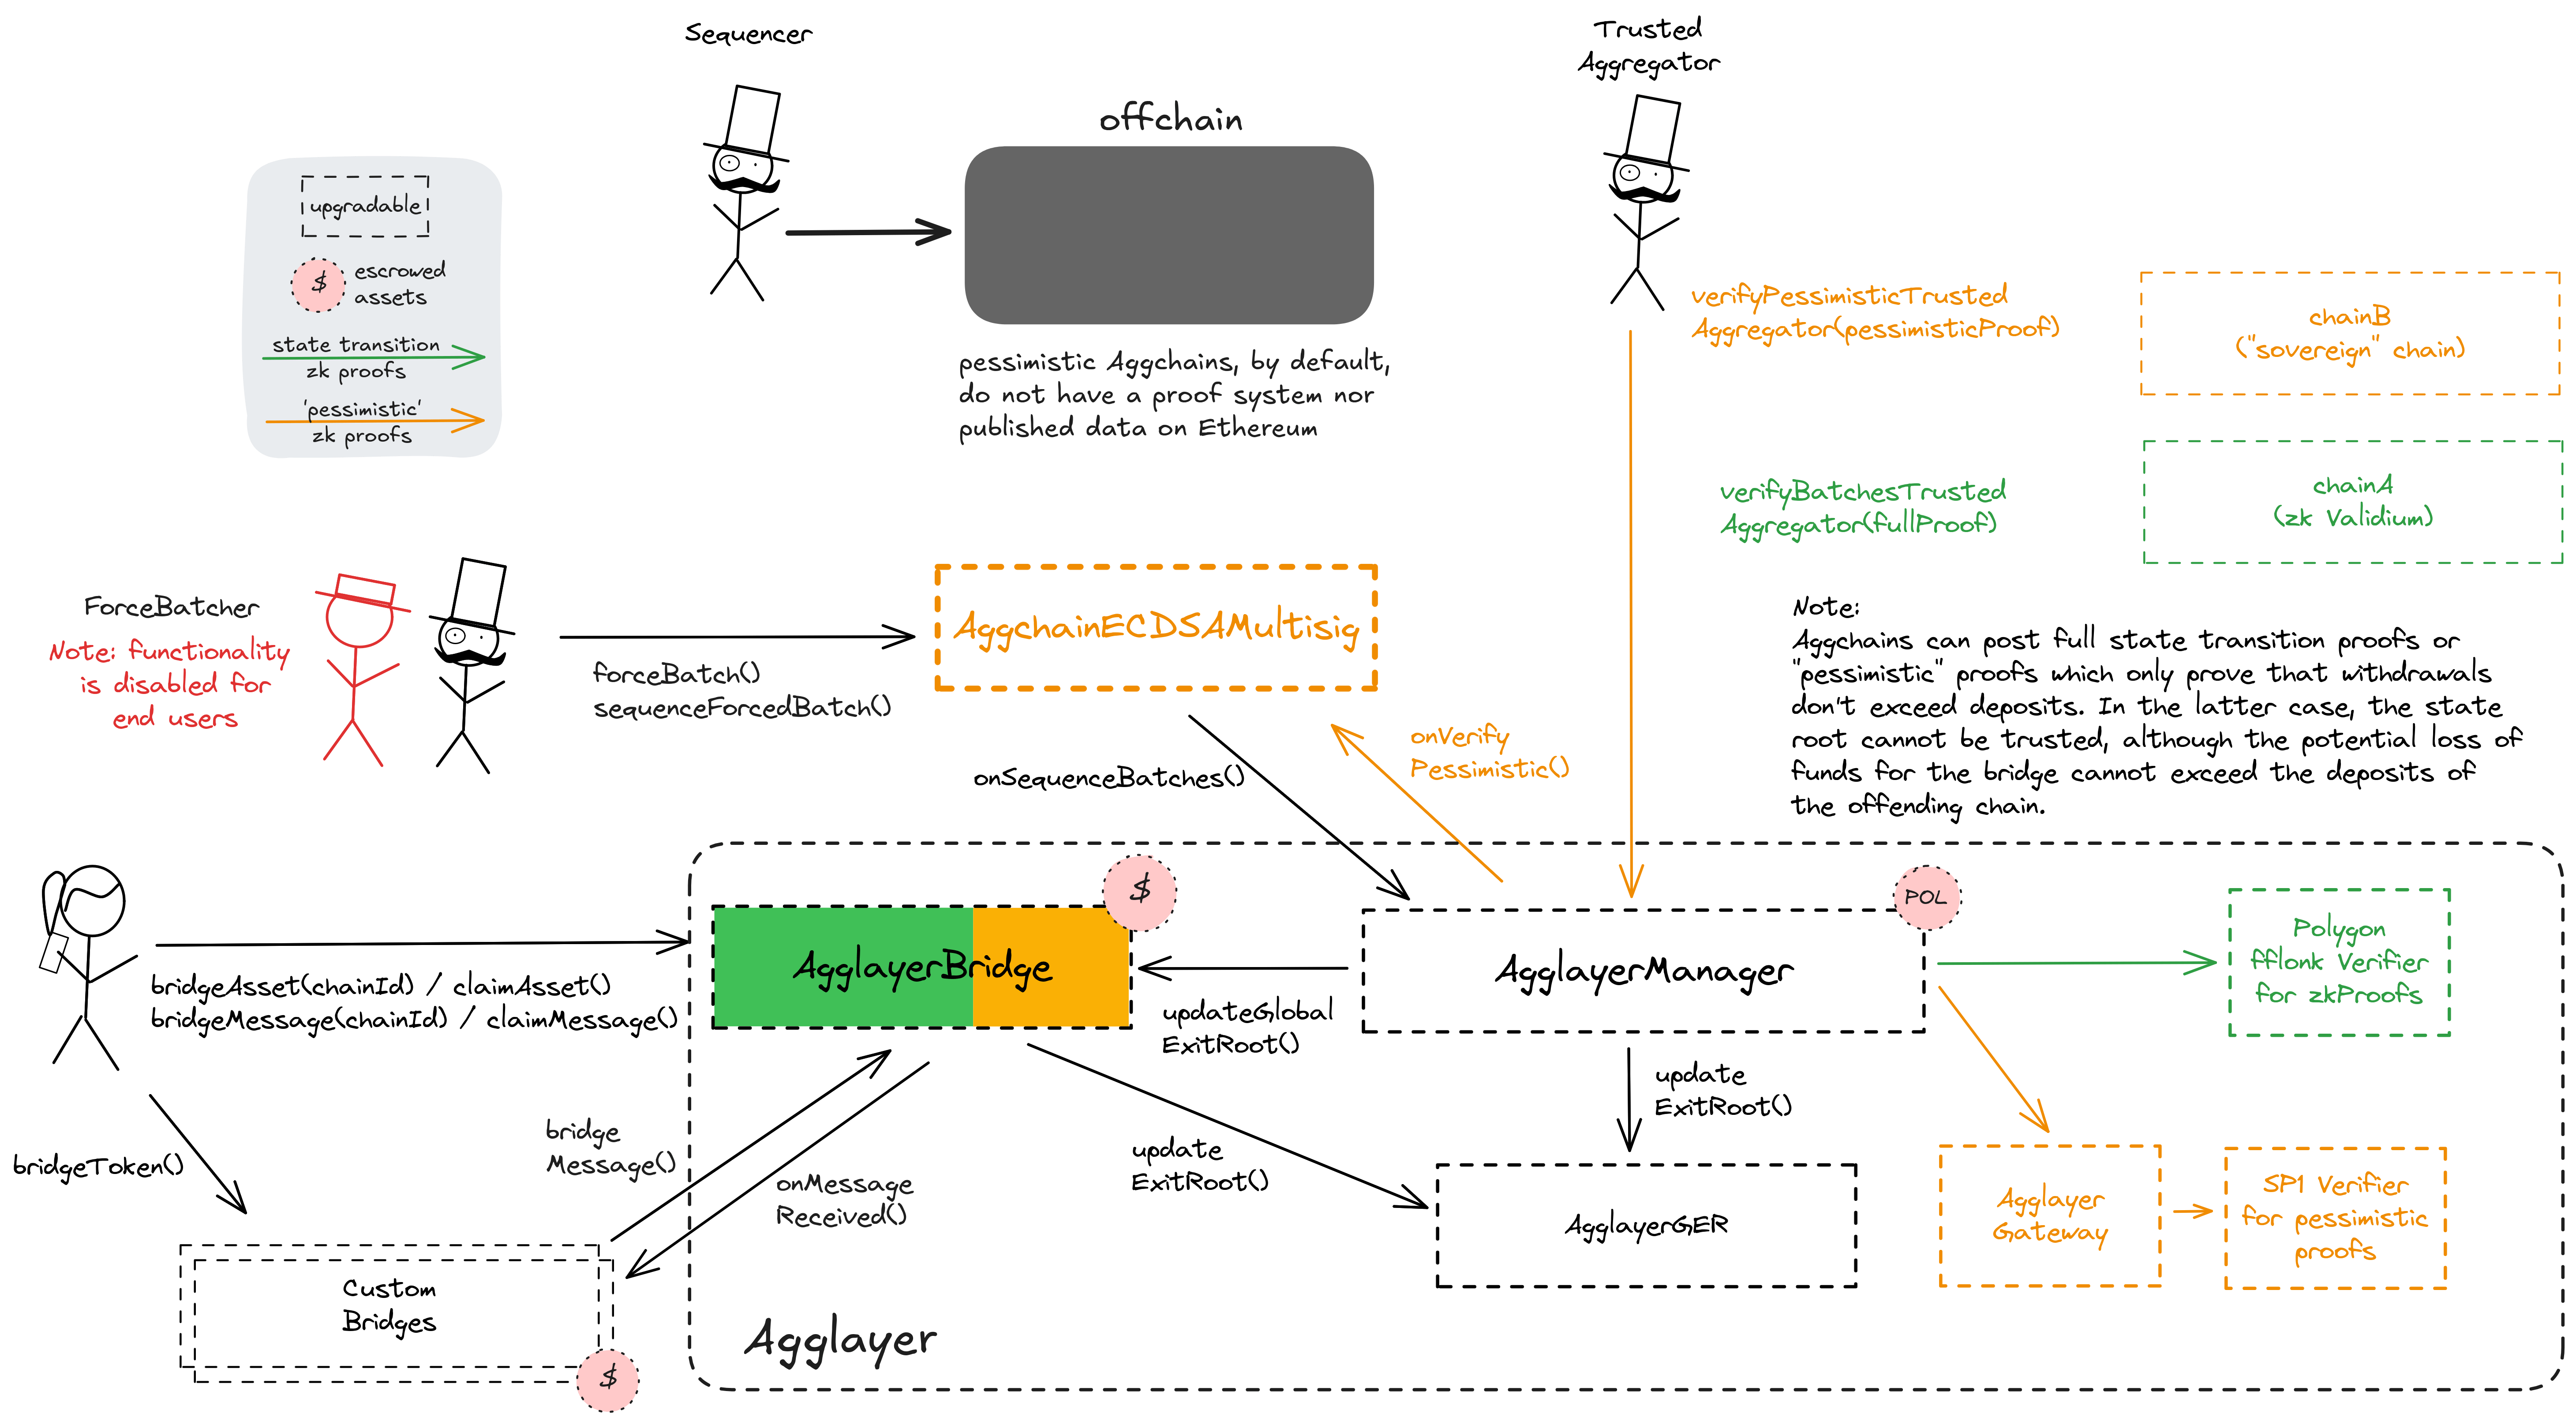
The central shared managing contract for Polygon Agglayer chains. This contract coordinates chain deployments and proof validation. All connected Layer 2s can be globally paused by activating the ‘Emergency State’. This can be done by the Polygon
- Can upgrade with no delay
- Aggchain
ECDSAMultisig
- Aggchain
A Multisig with 6/8 threshold.
- Can interact with AgglayerManager
- activate the emergency state in the Polygon
Rollup Manager and in the shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. immediately, effectively pausing all projects connected to them and making system contracts instantly upgradable
- activate the emergency state in the Polygon
Participants (8):
0xFe45…2e4b0xaF46…261D0xBDc2…FEFf0x4c16…88910x3ab9…D6220x49c1…0E860x9F7d…86A00x2188…1C28A Multisig with 3/5 threshold.
- Can interact with AgglayerManager
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the Polygon
Rollup Manager
- deploy new projects that use predefined rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. types (implementations) and connect them or other Agglayer chains to the Polygon
- Can interact with Aggchain
ECDSAMultisig - replace the aggchainSigners and the signature threshold (which sign the state transitions of this aggchain), switch to the default signers of the AgglayerGateway, upgrade the aggchain to a newer rollupA blockchain that inherits consensus and data availability from another blockchain called L1. Rollups enable trust minimized bridges with the base layer via proof systems, either optimistic or zero-knowledge. A rollup without a bridge, or without considering the bridge, is called a sovereign rollup. type of the same aggchain type registered in the AgglayerManager, set the aggchain metadata manager and transfer the aggchainManager role
- set the trusted sequencerA party responsible for ordering and executing transactions on the rollup. The sequencer verifies transactions, compresses the data into a block, and submits the data related to it to enable state reconstruction to Ethereum L1 as a single transaction. The data can be either transaction data or state diffs. address
- Can interact with Aggchain
ECDSAMultisig - sign state transitions (replaces state validation for this aggchain)
- Can interact with AgglayerManager
- Permissioned to post new state rootsA cryptographic hash succinctly representing a state using a Merkle tree. and global exit roots accompanied by ZK proofs
Ethereum
System contract defining the Haust NetworkA constellation of nodes (peers) that communicate via a peer-to-peer protocol, for example, in propagating transactions and blocks to other nodes. Aggchain logic. It only enforces bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. accounting (pessimistic) proofs to protect the shared bridge while the Aggchain state transitions are not proven. They must instead be signed by 1 aggchainSigner(s).
- Roles:
- admin: AgglayerManager, EOA 1
- aggchainManager: EOA 1
- aggchainSigners: EOA 2
A verifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. gateway for pessimistic proofs. Manages a map of chains and their verifier keys and is used to route proofs based on the first 4 bytes of proofBytes data in a proof submission. The SP1 verifier is used for all proofs.
- Roles:
- addPpRoute: Timelock; ultimately Polygon
Admin Multisig - admin: Shared
Proxy Admin; ultimately Polygon Admin Multisig - aggchain
Default : PolygonVKey Admin Multisig - alMultisig: Polygon
Admin Multisig - freezePpRoute: Polygon
Admin Multisig
- addPpRoute: Timelock; ultimately Polygon
The shared bridgeA message-passing protocol between two blockchains. At its most basic, a token bridge consists of a smart contract which can escrow funds on one side of the bridge, and instruct the release or minting of corresponding assets on the other side, but bridges could also support arbitrary messages. How these instructions are validated is a critical factor in assessing the trust assumptions of a bridge. contract, escrowing user funds sent to Agglayer chains. It is usually mirrored on each chain and can be used to transfer both ERC20 assets and arbitrary messages.
- Roles:
- admin: Shared
Proxy Admin; ultimately Polygon Admin Multisig - proxied
Tokens : Timelock; ultimately PolygonManager Admin Multisig
- admin: Shared
All supported tokens in this escrow are included in the value secured calculation.
A merkle treeA hash-based data structure in which each leaf node is a hash of a block of data, and each non-leaf node is a hash of its children. The root of the tree is a cryptographic fingerprint of the entire data structure. Merkle trees (Merkle Patricia Tries) are used in Ethereum to efficiently store key-value pairs. storage contract aggregating state rootsA cryptographic hash succinctly representing a state using a Merkle tree. of each participating Layer 2Layer 2 (L2) is a category of technical solutions aimed to scale the base layer in a trust minimized way. This category includes solutions like rollups as well as state channels and plasma. Other solutions are able to scale further, but with the introduction of additional trust assumptions, which are therefore not trust minimized. Sometimes the term Layer 2 is used to refer to include these solutions too, like validiums and optimiums, but to distinguish between trust minimized and non trust minimized solutions they are often referred to as "light" L2s, opposed to "strong" L2s like rollups., thus creating a single global merkle root representing the global state of the Agglayer, the ‘global exit root’. The global exit root is synchronized to all connected Layer 2s to help with their interoperabilityRefers to the capability of different blockchain networks to communicate and share data. It enables the transfer of assets and information between blockchains, facilitating functionality and collaboration between blockchain ecosystems..
- Roles:
- admin: Shared
Proxy Admin; ultimately Polygon Admin Multisig
- admin: Shared
A timelock with access control. In the case of an activated emergency state in the AgglayerManager, all transactions through this timelock are immediately executable. The current minimum delay is 3d.
- Roles:
- timelockAdmin: Polygon
Admin Multisig (no delay if in emergency state), Timelock (no delay if in emergency state); ultimately Polygon Admin Multisig (no delay if in emergency state)
- timelockAdmin: Polygon
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v5.0.0).
Extension contract of the AgglayerBridge for asset metadata…
VerifierAn entity in a ZK-Rollup, often a smart contract, that verifies zero-knowledge proofs submitted by a prover. contract for SP1 proofs (v6.1.0).
The current deployment carries some associated risks:
Funds can be stolen if a contract receives a malicious code upgrade. There is no delay on code upgrades (CRITICAL).